
Summary
API
Submitted URL: https://project-dapp.vercel.app/
AI Security Verdict
High Risk
Confidence: 85%
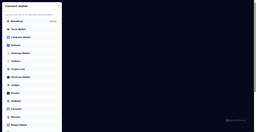
Wallet-connect/'synchronize wallet' lure on a free vercel.app subdomain, matching a threat-intel report of a wallet drainer. Do not connect a wallet or sign anything; avoid entirely.
Risk Factors (5)
Details
Page Title
ProjectDappsMainNet
Scan Type
public
Domain Name Analysis
The domain 'project-dapp.vercel.app' uses the application-focused generic top-level domain (.app), featuring subdomain 'project-dapp'. The second-level label 'vercel' is 6 characters long holding two vowels versus 4 consonants. Splitting it apart reveals two words: ver, cel. Average segment length settles at three characters. No strong language cues emerged from the frequency lists.
Screenshot

Other pages on this site
Page Load Overview
Language Analysis
Primary Language
Detection Details
Website Classification
Primary Category
All Detected Categories
Detected Features
Domain & IP Information
| Requests | IP Address | Location | AS Autonomous System |
|---|---|---|---|
| 2 | 64.29.17.3Aws · CLOUD | United States | AS16509Amazon.com, Inc. |
| 2 | 216.198.79.67Aws · CLOUD | United States | AS16509Amazon.com, Inc. |
| 2 | 64.29.17.67Aws · CLOUD | United States | AS16509Amazon.com, Inc. |
| 6 | 3 | - | - |
Detected Technologies5
Content Similarity HashesFor malware variant detection
TLSH (Trend Micro Locality Sensitive Hash)
Specialized for malware detection and similarity analysis
ssdeep (Context Triggered Piecewise Hashing)
Detects similar content even with modifications
sdhash (Similarity Digest Hashing)
High-precisionHigh-precision similarity detection for forensic analysis
These hashes enable detection of similar websites and malware variants by comparing content similarity even when exact matches aren't found.
Image Hashes
Perceptual Hashes
Other Hashes
Scan History
Scan history not available
Unable to load historical scan data