
Summary
API
Submitted URL: https://raydiumtoken-en.firebaseapp.com/
AI Security Verdict
Confirmed Scam
Confidence: 88%
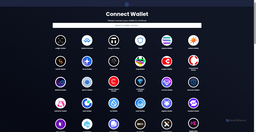
Counterfeit Raydium swap page on unrelated firebaseapp.com hosting, flagged as phishing and using 'Connect Wallet' / 'Claim Airdrop' lures typical of crypto-draining scams. Do not connect a wallet.
Risk Factors (5)
Details
Page Title
Swap Raydium
Scan Type
public
Domain Name Analysis
The domain name 'raydiumtoken-en.firebaseapp.com' uses the commercial generic top-level domain (.com), featuring subdomain 'raydiumtoken-en'. The registrable portion 'firebaseapp' spans 11 characters with 5 vowels and six consonants. Segmentation suggests three words: fire, base, app. Median word length comes out to 4 characters. No strong language cues emerged from the frequency lists.
Screenshot

Other pages on this site
Page Load Overview
Language Analysis
Primary Language
Detection Details
Website Classification
Primary Category
All Detected Categories
Detected Features
Domain & IP Information
| Requests | IP Address | Location | AS Autonomous System |
|---|---|---|---|
| 2 | 199.36.158.100Fastly · CDN | United States | AS54113Fastly, Inc. |
| 2 | 1 | - | - |
Content Similarity HashesFor malware variant detection
TLSH (Trend Micro Locality Sensitive Hash)
Specialized for malware detection and similarity analysis
ssdeep (Context Triggered Piecewise Hashing)
Detects similar content even with modifications
sdhash (Similarity Digest Hashing)
High-precisionHigh-precision similarity detection for forensic analysis
These hashes enable detection of similar websites and malware variants by comparing content similarity even when exact matches aren't found.
Image Hashes
Perceptual Hashes
Other Hashes
Scan History
Scan history not available
Unable to load historical scan data